Zoho One - SAML My Page SSO Configuration - RSA Ready Implementation Guide
Last Modified: 2024-05-30
Configure RSA Cloud Authentication Service
Perform these steps to configure RSA Cloud Authentication Service using My Page SSO.Procedure
- Enable My Page SSO by accessing the RSA Cloud Admin Console > Access > My Page > Single Sign-On (SSO). Ensure it is enabled and protected using two-factor authentication - Password and Access Policy.
- On the Applications > Application Catalog page, search for Zoho One and click Add to add connection.
- On the Basic Information page, enter a name for the configuration in the Name field and click Next Step.
- In the Connection Profile section, select the IdP-initiated option.
- Specify the Service Provider details in the following format:
- Assertion Consumer Service (ACS) URL: https://accounts.zoho.in/signin/samlsp/<application Id>.
- Service Provider Entity ID: <Zoho Entity ID>.
Note: Refer to the Zoho One configuration section to obtain the Assertion Consumer Service (ACS) URL and provide Entity ID as 'Zoho.in' in the RSA platform.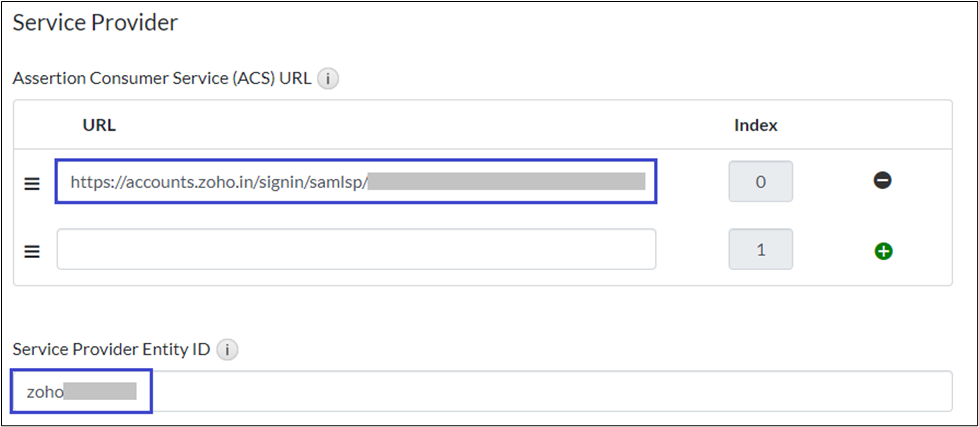
- In the SAML Response Protection section, select IdP signs assertion within response, and download the certificate by clicking Download Certificate.
- Under the User Identity section, select Show Advanced Configuration, then configure Identifier Type and Property as follows:
- Identifier Type: Auto Detect
- Property: Auto Detect
- Click Next Step.
- Choose your desired Access Policy for this application and click Next Step > Save and Finish.
- On the My Applications page, click the Edit dropdown and select Export Metadata to download the metadata.
- Click Publish Changes to save your settings. After publishing, your application will be enabled for SSO.
Configure Zoho One
Perform these steps to configure Zoho One.Procedure
- Log in to Zoho One with admin credentials.
- Click on the Gear icon in the top right corner.
- Navigate to Security > Custom Authentication then click Add IdP.
- Provide the details for Display Name and Choose Groups.
See the Notes section to learn how to create Groups.
- Select SAML radio button and copy the ACS URL.
- Provide the mandatory details and click Save.
- Sign-in URL – The value of SingleSignOnService URL, obtainable from the metadata file downloaded from the RSA platform.
- Verification Certificate - Upload the certificate downloaded from the RSA platform.
Notes
Follow the steps to create Groups:- Click on the gear icon in the top right corner.
- Navigate to Directory > Groups > Add Group.
- Provide the Group Name, add members, then click Add.
- Click Done
Return to Zoho One - RSA Ready Implementation Guide



